-
Socket discovered a total of 319 extensions available in Chrome that manipulate user searches and attracted over 13 million installations over the years.
-
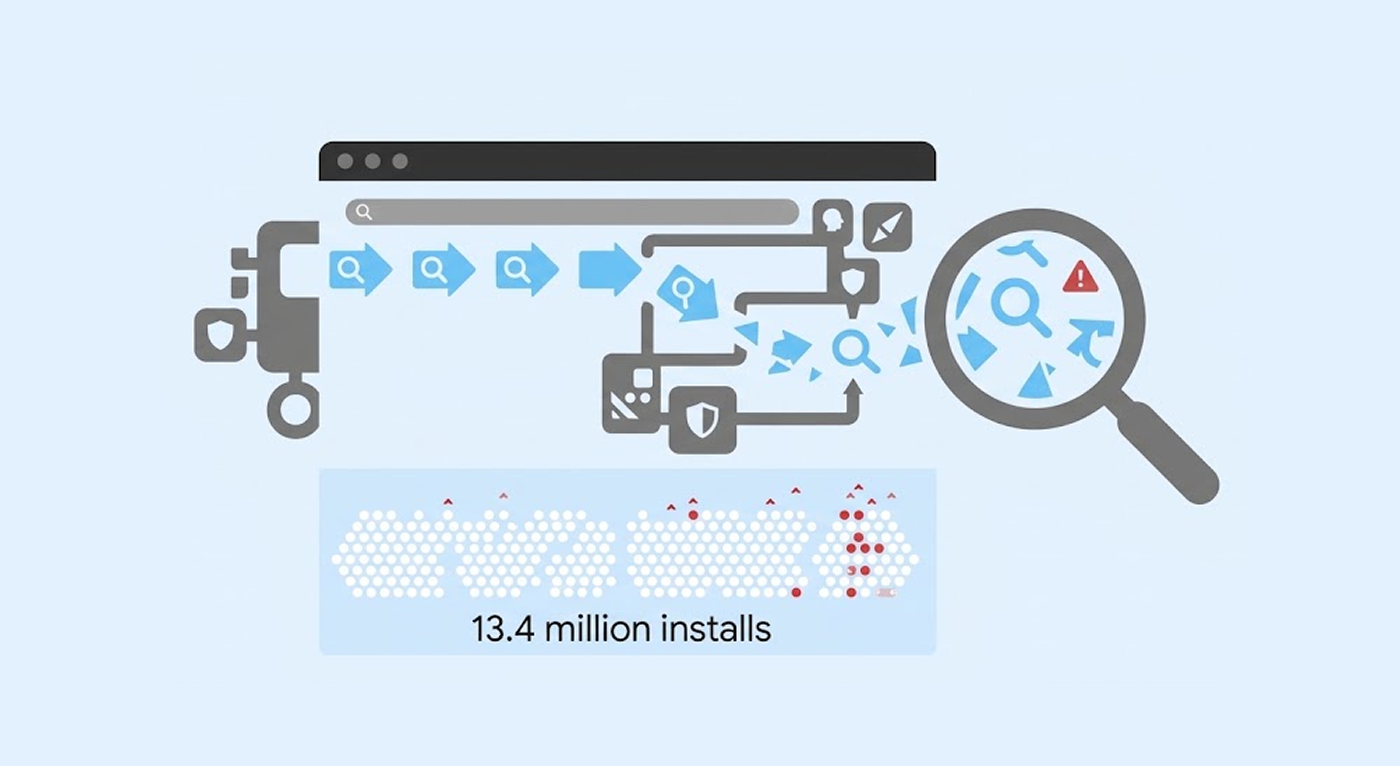
These extensions work by routing all user searches via devices that the operators control, earning from Yahoo and Bing referral payments.
-
Users may choose to uninstall unknown Chrome extensions, along with checking and resetting their search engine default settings.
Security researchers have found a large network of Chrome extensions that secretly take over search results. These extensions have racked up about 13.4 million installs over the past decade. They route every search through servers controlled by the people behind them.
The researchers at Socket published their findings on October 29, 2026. The lead researcher is John Tuckner. His earlier work in April 2025 found 57 such extensions. The new report adds 264 more, bringing the total to 319.
How the extensions trick users
The extensions present themselves as valuable applications. They offer to help with PDF conversions, finding things manually, or returning search results using artificial intelligence. They make sure not to show up in regular Chrome Web Store search results. Instead, they make it to users through pop-ups on barely popular websites.
After installation, they change the default search engine in the browser. Chrome even has a built-in feature that allows this. There are extensions that require no special background code and don’t need any permission.
The process of installation is the trick here. Most users never notice it happening. They make a search request and get the results, not suspecting a change in anything. But the extension does its job in silence in the background.
Furthermore, the extensions evade suspicious & attention by choosing simple names for themselves and simple icons. They also do not ask for permission to access any browsing history or any personal data. This keeps them under the radar of security tools that flag suspicious permission requests.
The researchers also found that many of these extensions share code. Different publishers used the same template with small changes. This pattern suggests a few operators built tools for many separate sellers.
What the operators gain
The main goal is money. Yahoo and Microsoft run programs that pay partners for search traffic. The operators attach their partner tags to each search. This earns them referral payments.
The proxy also gives them control. They can change the destination at any time without updating the extension. In one test, six identical searches through one extension ended up in four different places.
Researchers warn this could lead to worse problems. The operators could send users to phishing pages or malware downloads. They have not observed this yet, but the setup allows it.
The earnings can add up fast – a single extension with 100,000 users can generate thousands of searches per day. Each search brings a small payment. Across 319 extensions, the total income could reach millions of dollars over the years.
Who is behind the campaign?
Socket linked about 111 extensions to a company called Intango LTD. These extensions reached roughly 2.2 million users. Another group called SecuryBrowse had 58 extensions and about 4.9 million users. These used security-themed names like Fire Shield and WatchTower.
A newer cluster called Bing-Search had 37 extensions and about 2.2 million users. Fifteen supposedly separate publishers updated their extensions within four days of each other in June this year. This showed they worked together.
The activity dates back to 2016, when a Yandex extension, based in Russian language, required users to search via a proxy. Subsequently, it reached 200,000 users before removal.
The long history matters. It proves that the method was ongoing for many years, despite product reviews in the stores. Every time a batch is taken down, new batches appear under different names. The operators clearly see take-downs as simply a cost of doing business.
What users should do?
Users should check their installed extensions. They should remove any they do not recognize. Further, they should remove those they are not aware of. More specifically, special attention should be paid to the search tools, PDF management programs, plus various security add-ons they have.
After removing unknown add-ons, they have to verify the default search engine and set it to the one they prefer to have. Doing a full antivirus scan is also a properly advised action here.
The majority of the identified extensions have already been deleted from the Chrome Web Store. However, new ones will keep coming. Users must be attentive to pop-up ads offering them free programs and tools.
Google has not commented on the full scope of the report. The company has removed extensions in the past after similar research. Also, it regularly runs a program for verifying the publishers, but this action still has not stopped such occurrences.
This is not the only recent warning about malicious Chrome extensions. Researchers have also uncovered fake extensions that stole data from more than 300,000 users.
Those who want to be on the safe side can limit their extensions to those they currently trust. They can also check the permissions after every update. These habits reduce the chance of a quiet switch.
