-
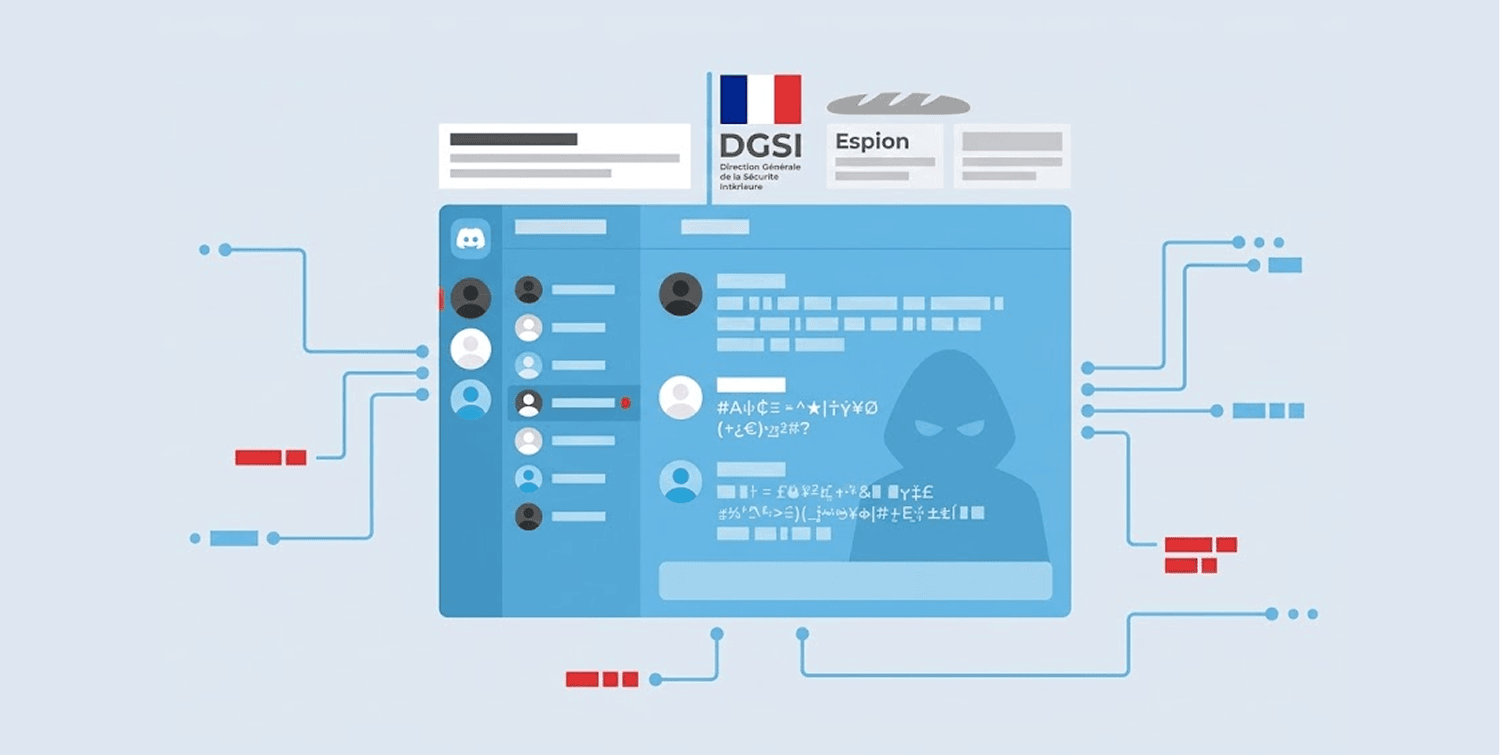
Security researchers entered a private Discord server of 1,400 young hackers they ironically named after France’s domestic intelligence agency.
-
A former French Interior Ministry intern was identified interacting with the network after his recent workplace removal.
-
Members used the satirical server to coordinate cyber-attacks, trade stolen personal data, and organize offensive operations.
Cybersecurity experts are examining an obscure internet organization comprising around 1,400 young computer hackers. The illegal organization also chose the name for its main Discord hub after the French General Directorate for Internal Security, an intelligence agency in France.
Authorities have revealed that the members of the group used this instant messaging platform to plan cyber-attacks & sell databases they steal. Furthermore, authorities identified a former intern of the Ministry of the Interior using this underground network after he lost his job.
Franco-Belgian joint research stomps underground hacker server
An independent joint research team that comprises Franco-Belgian security analysts successfully stomped on the private chat server to uncover their internal operations. The underground community acts as a hub where high school students & young university coders gather on Discord.
Inside the invitation-only server, administrators created a mock organizational structure that appeared like real state intelligence departments. Members earn internal server ranks while joining hands in planning all forms of bad operations like live website defacements, credential harvesting, plus database trading operations.
Apart from that, the covert investigation found out that those who participate in the server share personally identifiable information, always & these are what they steal from private citizens. The chat logs document active discussions about techniques of database exploitation, setups for proxy routing, & methods to carry out social engineering attacks.
Due to these findings, security researchers forwarded detailed intelligence logs directly to national law enforcement agencies that monitor cybercrime networks.
Former interior ministry intern part of the covert Discord hacking community
Security analysts tracking the chat server identified an individual who recently worked as an intern inside the Ministry of the Interior. Government officials recently pushed the young worker out of his role following administrative review procedures.
However, investigators discovered that the former intern was active in this underground hacking hub during his ministry tenure. His digital accounts showed he was always interacting with key server administrators who oversee offensive campaign channels.
While authorities have not told the public whether official government systems faced direct compromise, his presence is a major concern. Intelligence analysts note that rogue staff members holding baseline administrative knowledge present a high risk to state networks.
Therefore, investigative agencies continue probing whether internal ministry documentation or confidential network access parameters were leaked.
Discord platform misuse and intelligence challenges in monitoring youth cybercrime
Many young people are turning to Discord as a tool for organizing criminal activities and distributing software. The platform features easy messaging, communication over the phone, and file transfer as an attraction for young people who know how to use technologies.
Similar campaigns have also used fake GitHub repositories to distribute BoryptGrab malware, showing how attackers can abuse legitimate developer platforms to spread malicious software.
In addition, underground administrators work with the help of bots that provide access to the servers only for a limited number of verified users. This advanced process requires intelligence specialists to use special methods of infiltration to monitor activities in underground platforms.
Moreover, law enforcement agencies face the difficulty of determining when it is appropriate to act in shutting down illicit online communities. Such closures are necessary to stop the process of data trading, but it deprives law enforcement agents of an important source of information.
However, Discord is always willing to cooperate with the authorities, as it can issue emergency takedowns of content.
Strengthening digital hygiene standards and insider risk mitigation strategies
The exposure of this youth hacking hub underscores the urgent need for stricter identity controls across sensitive public institutions.
Cybersecurity professionals propose the introduction of some technology measures such as multi-factor authentication, privileged access management, and behavioral monitoring of users within state networks.
In addition to the technical measures, institutions of the government should improve their background check methods for their temporary employees, subcontractors, and intern students. They can do so through a strict zero-trust access policy that ensures that short-term personnel access only necessary operational data files.
To deal with young cybercriminals effectively, it is necessary to implement early intervention measures and programs, with decisive legal enforcement actions against persistent offenders. Guiding talented young programmers toward ethical bug hunting channels prevents them from falling into criminal online ecosystems.
As underground groups tend to mimic state structures, public institutions should enhance digital defenses against external threats and internal leaks.
